

Setting up your identity provider
Follow the steps for your provider to create the app and collect the values you enter in Base44. Microsoft Entra ID and Okta each need a few extra steps, so they have their own guides.Microsoft Entra ID
Uses a dedicated app registration, and also supports SCIM provisioning.
Okta
Uses an OIDC app plus a couple of authorization-server settings.
Google Workspace
Google Workspace
Create an OAuth 2.0 client in Google Cloud, then enter its credentials in Base44.To create the Google app:
- In the Google Cloud Console, create an OAuth 2.0 Client ID of type Web application.
- Under Authorized redirect URIs, add your workspace redirect URI.
- Copy the Client ID and Client Secret.
GitHub
GitHub
Create a GitHub OAuth app, then enter its credentials in Base44.To create the GitHub app:
- In GitHub Developer Settings, create an OAuth app.
- Set the Authorization callback URL to your workspace redirect URI.
- Copy the Client ID and generate a Client Secret.
Any other OIDC provider
Any other OIDC provider
Connect any OpenID Connect provider by creating a client and entering its details in Base44.To create the app:
- Create an OIDC client with your provider, using your workspace redirect URI.
- Copy the Client ID and Client Secret.
- Find your provider’s Discovery URL, or its individual OIDC endpoints.
Adding your credentials in Base44
Once you have your provider’s credentials, add them to your workspace. For Microsoft Entra ID and Okta, follow their dedicated guides above instead, which include this step. To add your SSO credentials:- Click your workspace name at the bottom left of your account.
- Click Settings.
- Click Authentication.
- Click Set Up next to Single Sign-on Configuration.
- In Select SSO Provider, choose your provider, or Advanced / Manual Configuration for another OIDC provider.
- Enter your Client ID and Client Secret, and keep Scope as
openid email profile. - For Advanced / Manual Configuration, also add your Discovery URL or the individual endpoints from your provider.
- Click Enable SSO.
Members can sign in once you verify their email domain. Set up verified domains and the default role in the same Authentication settings.
Testing your SSO login
Confirm that sign-in works before you roll SSO out to your team. The first time someone signs in, Base44 adds them to the workspace automatically with your default role. To test SSO:- Log out of Base44, or open a private browser window.
- Go to your workspace’s login page.
- Enter an email address from one of your verified domains. Base44 then shows the SSO option for that domain.
- Click Log in with SSO and sign in through your identity provider.
- Confirm that you are redirected back to Base44 and added to the workspace as a member with your default role.
Removing your SSO setup
Removing your SSO setup turns off SSO for your workspace and deletes your identity provider, along with the credentials you saved. Remove it when your team stops signing in to Base44 through that provider, or when you want to start your setup again from the beginning. After you remove it, your members sign in to Base44 the way they did before you set up SSO, for example with Google or with their email and password. If your apps let people sign in with your workspace SSO, that option goes away in those apps too.If you only want to pause SSO, turn off the toggle next to Single Sign-on Configuration instead. Your provider details stay saved, and you can turn it back on anytime.
- Click your workspace name at the bottom left of your account.
- Click Settings.
- Click Authentication.
- Under Single Sign-on Configuration, next to your provider, click Configure.
-
Click Clear to empty the form.
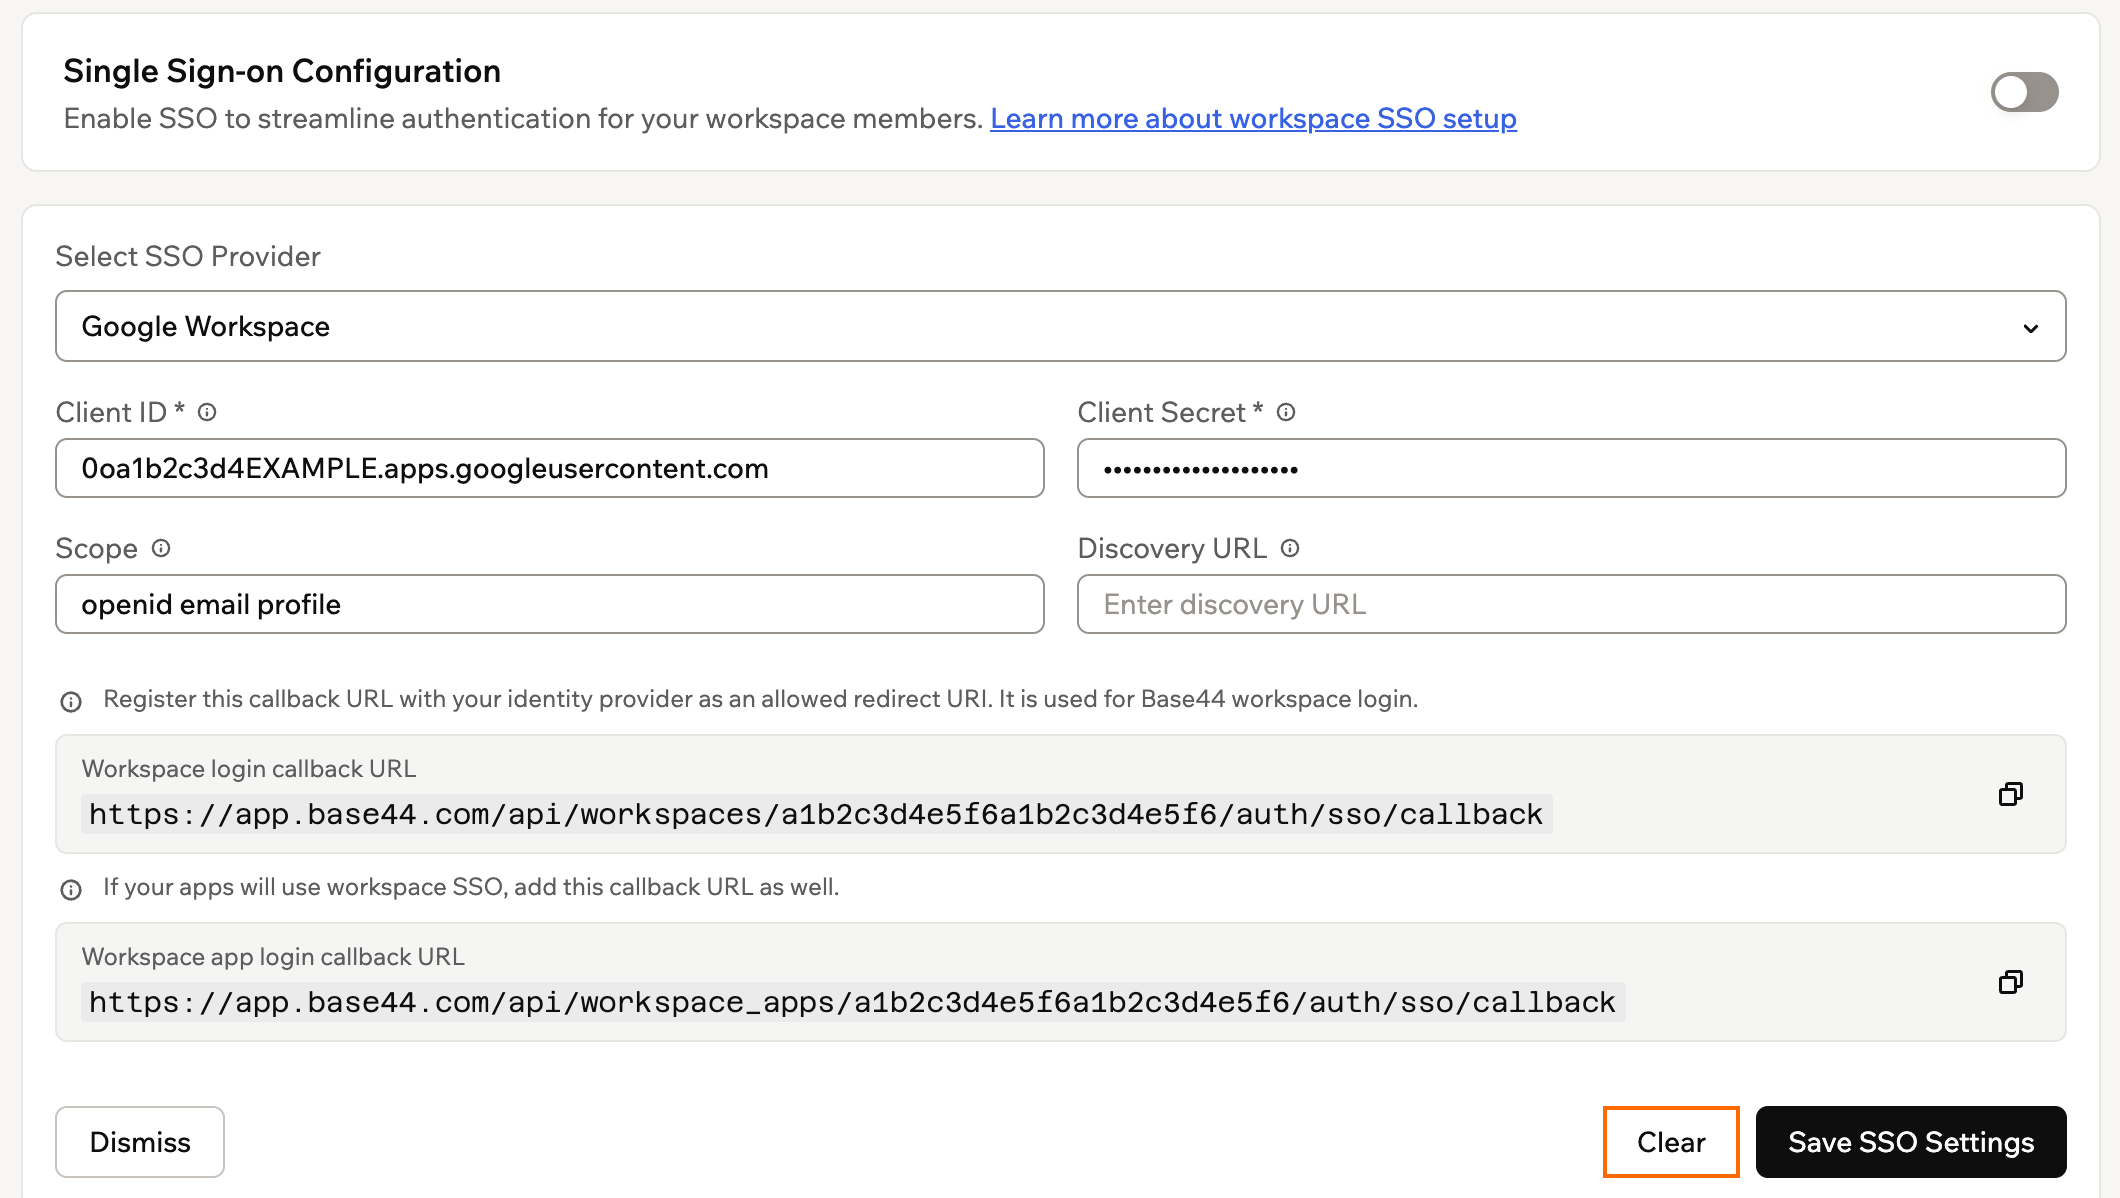
Clearing your SSO setup
- Click Save SSO Settings.
- In the confirmation, click Remove setup.