> ## Documentation Index
> Fetch the complete documentation index at: https://docs.base44.com/llms.txt
> Use this file to discover all available pages before exploring further.
> ## Agent Instructions
> Internal links on these pages omit the .md extension. Append .md to a docs page URL, or send an Accept: text/markdown header, to get that page as markdown.
# Managing workspace secrets
> Create workspace API keys with only the permissions you choose, block members' personal account API keys, and set a policy for the personal access tokens used.
Workspace secrets let you create and manage API keys for programmatic access to your workspace. Use these keys to deploy apps, provision app users, or create sign-in tokens for embedded apps. On the Enterprise plan, you can also use them to stream audit logs, pull workspace data through the Monitoring API, and read or manage users over SCIM. These aren't included in the Business plan. Each key carries only the permissions you give it.
Keys are workspace-owned, so they stay active even if the member who created them leaves the workspace.
**Important:**
* Workspace secrets are available on an Enterprise plan (Business or Enterprise).
* Only workspace owners and admins can view and manage secrets.
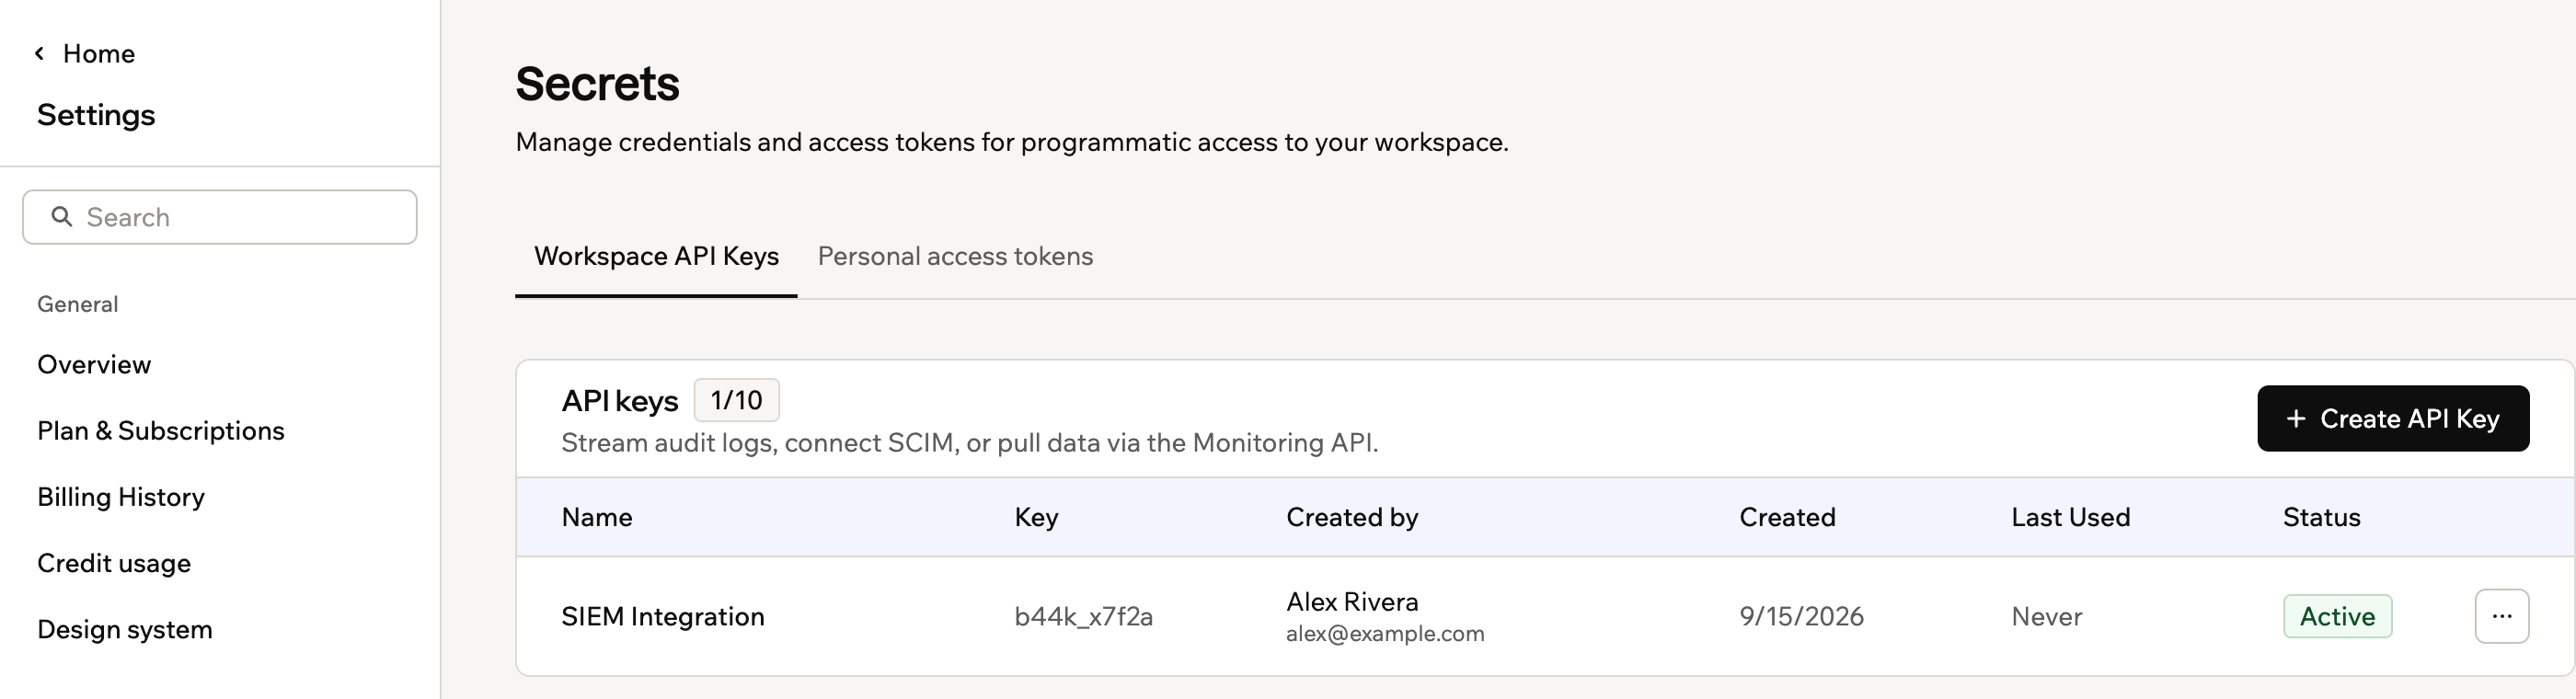 For a full list of supported APIs, [see the API reference](/developers/references/audit-logs-api/get-started/overview).
***
## Creating an API key
You can create up to 10 API keys per workspace.
**Important:**
* Copy your key immediately after creating it. You can't see it again.
* Treat it like a password: it grants access to your workspace data via the API.
**To create an API key:**
1. Click your workspace name at the bottom left and click **Settings**.
2. Click **Secrets** in the sidebar.
3. Click **+ Create API Key**.
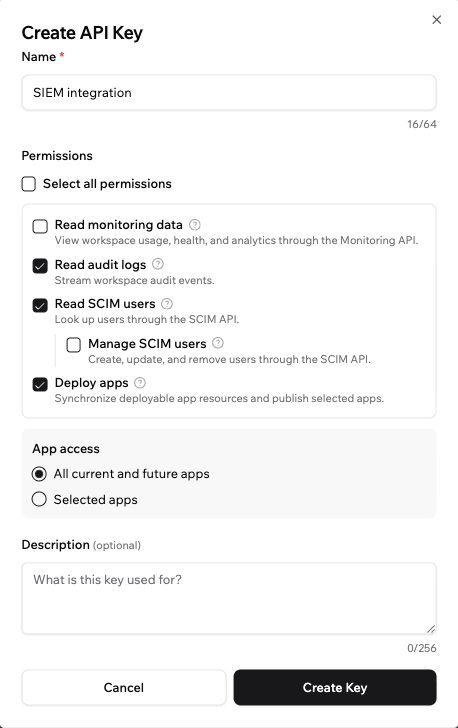
4. Enter a name for the key (required) and an optional description.
5. Under **Permissions**, select the scopes this key should have. See [Choosing permissions](#choosing-permissions) for what each one grants.
6. If you select **Deploy apps**, set its **App access** to **Selected apps** and choose the apps, or to **All current and future apps**.
7. Click **Create Key**.
8. Copy the key and store it somewhere safe.
9. Click **Done**.
 ***
## Choosing permissions
Each API key has one or more permissions, called scopes, that control which parts of your workspace it can access. Give a key only the permissions the integration needs.
| Permission | What it allows |
| - | - |
| **Read monitoring data** | View workspace usage, health, and analytics through the [Monitoring API](/developers/references/monitoring-api/get-started/overview). |
| **Read audit logs** | Stream workspace audit events through the [Audit Logs API](/developers/references/audit-logs-api/get-started/overview). |
| **Read SCIM users** | Look up the users provisioned to your workspace through [SCIM](/Enterprise/SCIM-provisioning). |
| **Manage SCIM users** | Create, update, and remove SCIM users. Requires **Read SCIM users**. |
| **Deploy apps** | Synchronize and publish apps in your workspace. |
| **Provision app users** | Give people access to apps in your workspace, or remove it. Used to [embed apps](/developers/white-label/embed-the-app). |
| **Mint embed sign-in tokens** | Create one-time tokens that open an app signed in as one of its users. Used to [embed apps](/developers/white-label/embed-the-app). |
For the **Deploy apps**, **Provision app users**, and **Mint embed sign-in tokens** permissions, choose which apps the key can reach:
* **Selected apps:** The key can only deploy the specific apps you choose.
* **All current and future apps:** The key can deploy any app in the workspace, including apps you add later.
You can make changes to a key at any time. To update its name, description, or permissions, edit the key from the **Secrets** page.
***
## Managing your API keys
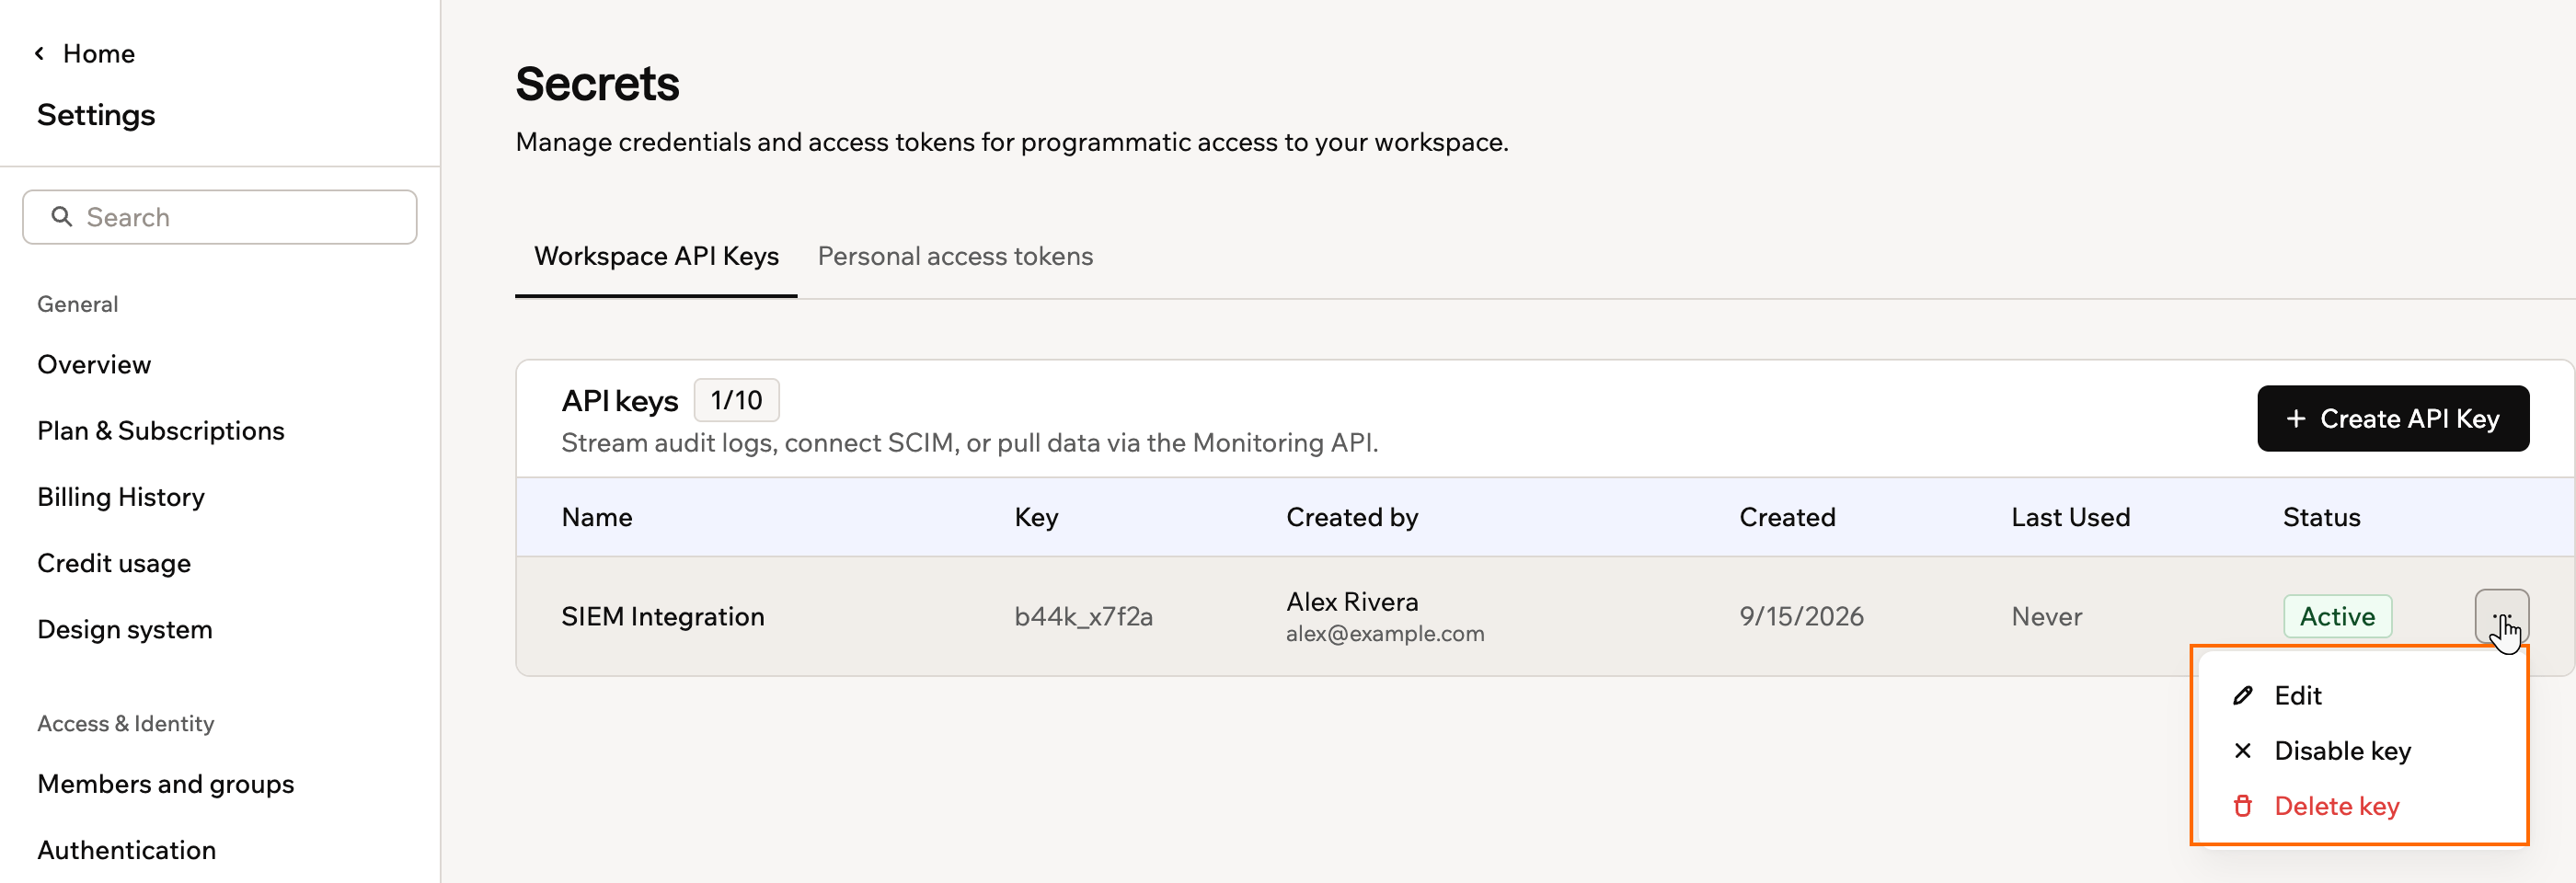
From the **Secrets** page, you can view all your keys along with who created them, when they were created, and when they were last used. Click the **More actions** icon next to a key to edit, disable, or delete it.
Creating, editing, enabling, disabling, and deleting a key are all recorded in your workspace [audit logs](/developers/references/audit-logs-api/get-started/overview), and actions taken with a key are attributed to it.
**To manage an API key:**
1. Click your workspace name at the bottom left and click **Settings**.
2. Click **Secrets** in the sidebar.
3. Click the **More actions** icon next to the key you want to manage and select an option:
* **Edit:** Update the key's name, description, or permissions.
* **Disable key:** Temporarily prevent the key from being used without deleting it.
* **Enable key:** Re-enable a previously disabled key.
* **Delete key:** Permanently remove the key. This cannot be undone, and anything using that key stops working straight away.
 ***
## Blocking personal account API keys
Alongside the workspace keys you create here, every Base44 user has their own personal account API key. While someone is a member of your workspace, their personal key can reach your workspace's apps and data. You can block personal keys so that only workspace API keys, which admins create and manage, can be used.
You can do this whether or not your workspace uses SSO. It is especially useful if you [require SSO for all workspace members](/Enterprise/SSO-for-enterprise-workspace#require-sso-for-all-workspace-members), because it closes the gap between how people sign in and how they can reach your data programmatically.
**Before you turn this on:**
* Blocking personal account API keys requires an Enterprise plan (Business or Enterprise).
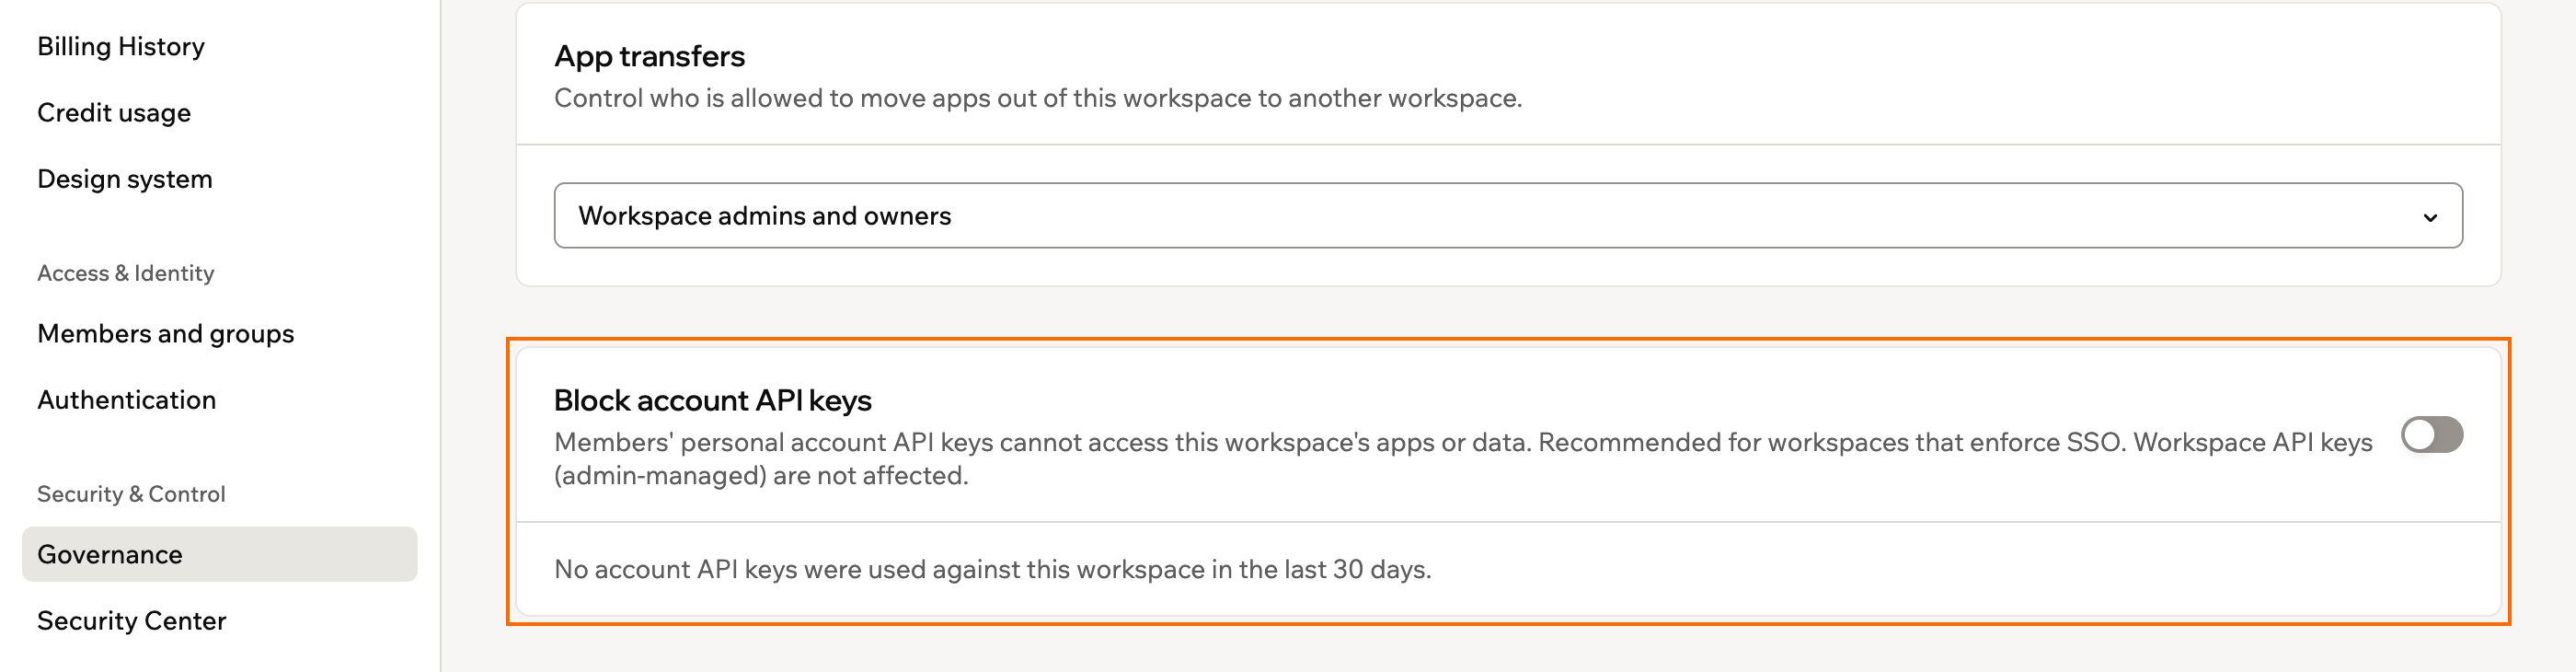
* The setting shows how many requests used a personal account API key against your workspace in the last 30 days, and how many members are actively using their keys, so you can see who this affects. You can review the full list in your [audit logs](/developers/references/audit-logs-api/get-started/overview).
* Workspace API keys are not affected, so anything built on an admin-managed key keeps working.
* App users signing in to your published apps are not affected.
**To block personal account API keys:**
1. Click your workspace name at the bottom left of your account.
2. Click **Settings**.
3. Click **Governance**.
4. Turn on **Block account API keys**.
 ***
## Governing personal access tokens
Members can create [personal access tokens](/Workspaces/Personal-access-tokens) to let their own scripts and tools reach your workspace's apps. A token acts as the member who made it and never exceeds their own permissions, and it stops working when they leave the workspace.
As an admin you decide whether tokens may be used in your workspace at all, and how much a token is allowed to do. The controls sit in the **Enable personal access tokens** card on the **Governance** page, and every member token created for the workspace is listed in **Secrets**.
**What to know before you set a policy:**
* Governing members' tokens requires an Enterprise plan (Business or Enterprise). Creating and using tokens works on every plan, so without this control members can still make them.
* Turning the card off suspends every member token immediately. Nothing a member built on one works until you turn it back on.
* Tightening a limit does not break tokens retroactively. A token that no longer fits is marked **Doesn't meet policy** and keeps working until someone disables it, so you choose when to cut it off.
* A member cannot re-enable a token that misses the policy, and cannot pick an option the policy does not allow when creating a new one.
### Setting the access token policy
The card carries a switch for tokens as a whole, and 2 limits that cap what any token may be. Each limit names the most a token is allowed to be, so choosing **Read-only** means nobody can create a token that changes data.
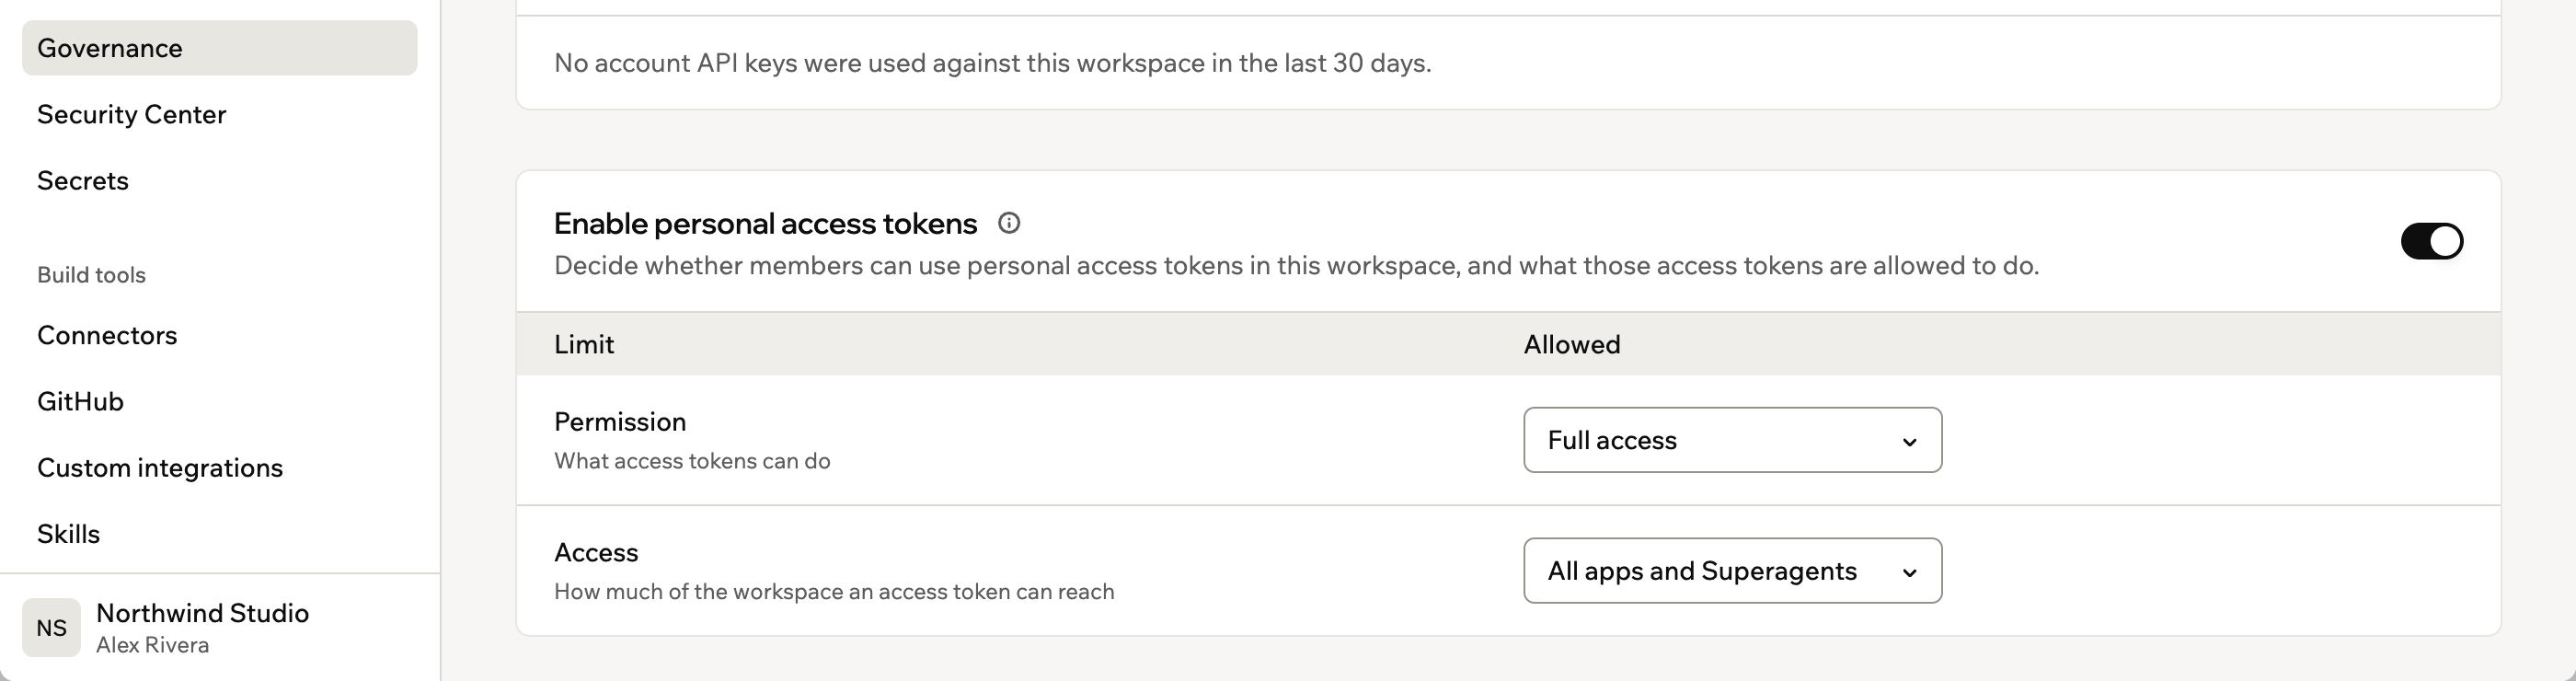 **To set your access token policy:**
1. Click your workspace name at the bottom left of your account.
2. Click **Settings**.
3. Click **Governance**.
4. Turn the **Enable personal access tokens** toggle on or off.
5. Next to **Permission**, choose the most a token may do: **Full access** or **Read-only**.
6. Next to **Access**, choose how much of the workspace a token may reach: **All apps and Superagents** or **One app or Superagent**.
### Reviewing members' access tokens
The card's footnote counts the member tokens that meet your policy and links straight to the full list. In **Secrets**, the **Personal access tokens in this workspace** table is admin only, and shows each token's owner, access, permission, status, and when it was last used. You can disable or delete any of them, but you cannot change one, since it belongs to the member who made it.
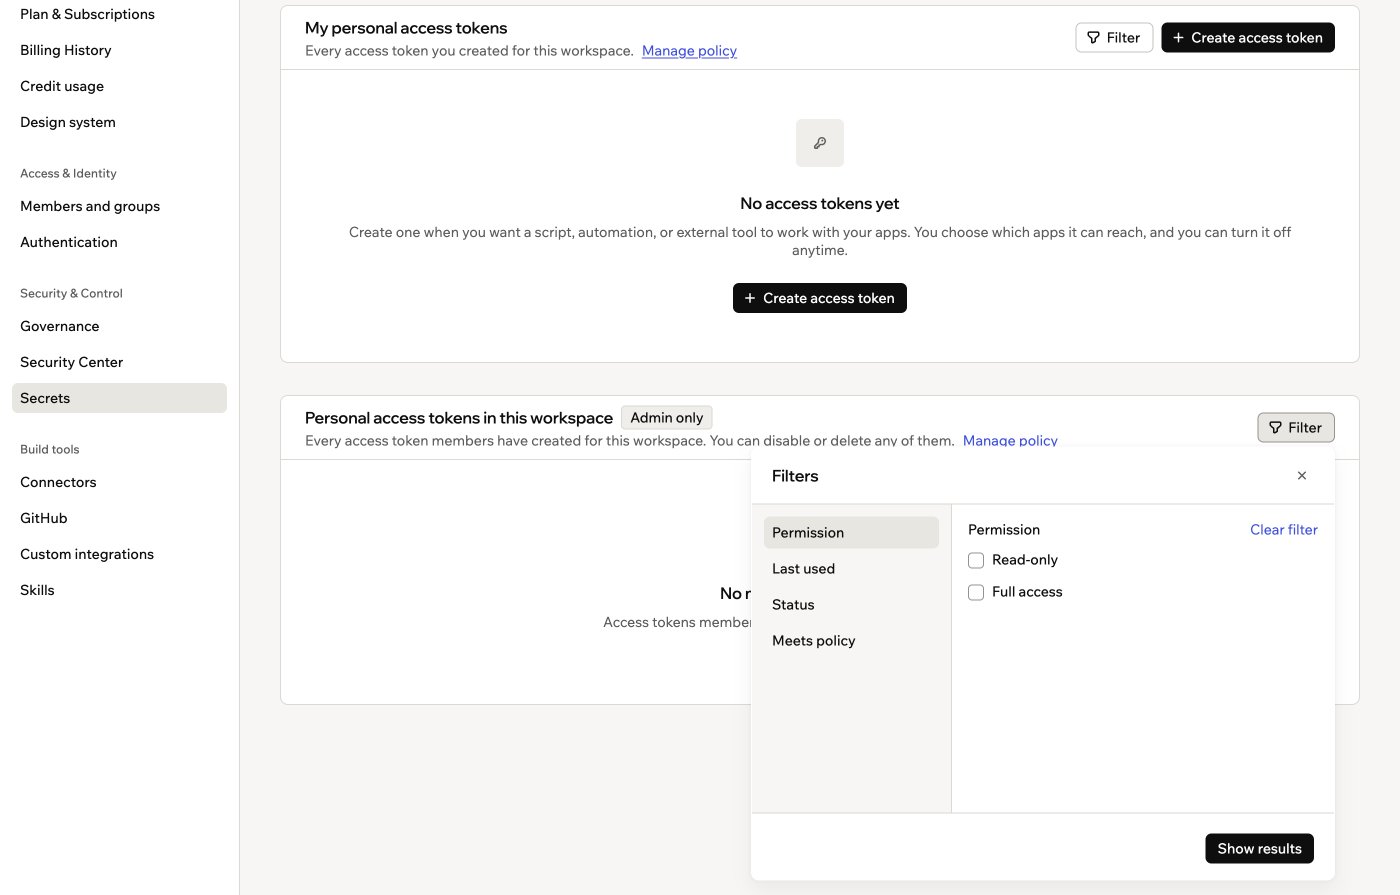 **To review and act on members' access tokens:**
1. Click your workspace name at the bottom left of your account.
2. Click **Settings**.
3. Click **Secrets**, then click the **Personal access tokens** tab.
4. Under **Personal access tokens in this workspace**, click **Filter** to narrow the list by permission, last used, status, or whether a token meets your policy.
5. Next to a token, click the **More actions** icon and click **Disable** or **Delete**.
This documentation is built and hosted on [Mintlify](https://mintlify.com), a developer documentation platform.